

Cybersecurity is entering a new phase of automation. OpenAI has just unveiled Daybreak, an artificial intelligence system designed to identify, analyze, and fix certain security vulnerabilities in just a few minutes. Behind this announcement lies a profound transformation in cyber defense practices, where AI agents are now capable of performing tasks that previously required hours or even days of human intervention.
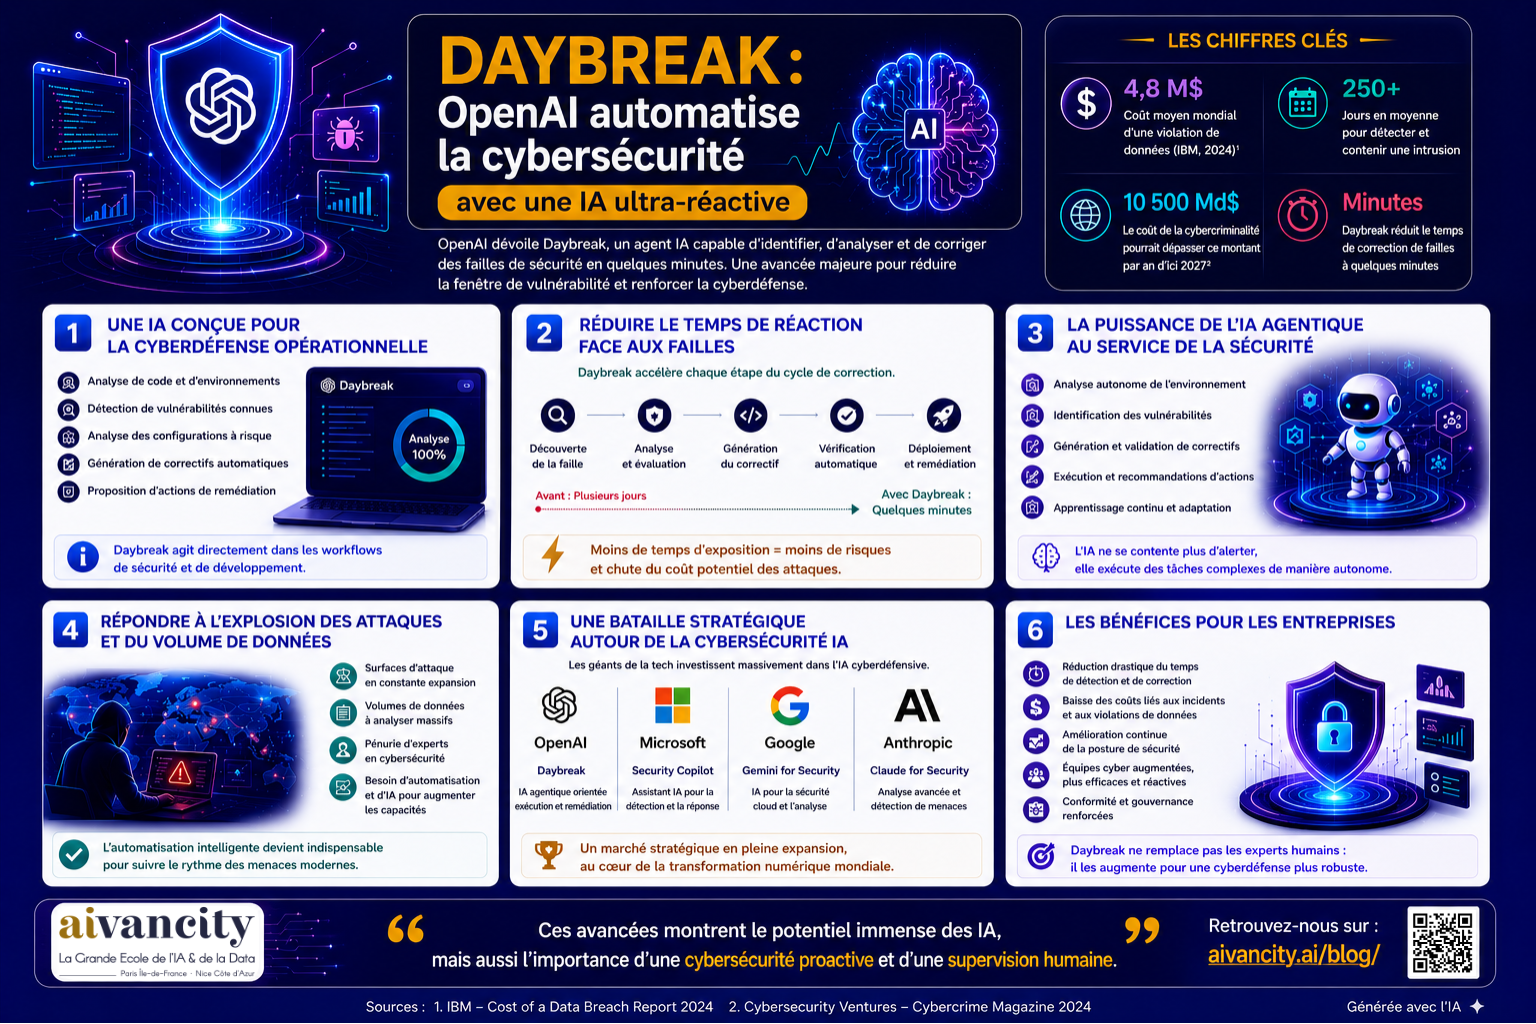
This trend comes at a time when cyberattacks are on the rise and companies are struggling to patch critical vulnerabilities quickly enough. According to IBM, the global average cost of a data breach now exceeds $4.8 million1, while the average time required to detect and contain a breach remains over 250 days in certain sectors. OpenAI aims to drastically reduce this window of vulnerability through agent-based AI applied to cybersecurity.
AI designed for operational cyber defense
Daybreak is more than just a chatbot designed to answer questions about IT security. The system functions as a specialized AI agent capable of analyzing code, inspecting systems, detecting suspicious behavior, and suggesting automated fixes.
The goal is to reduce the time between the discovery of a vulnerability and its actual resolution. Today, many companies accumulate unpatched vulnerabilities due to a lack of sufficient human resources or continuous monitoring capabilities. Daybreak aims to automate part of this process by integrating directly into security and software development workflows.
According to OpenAI, the system can:
- identify known vulnerabilities,
- analyze high-risk scenarios,
- detect anomalies in software environments,
- generate patches,
- and propose appropriate corrective actions.
This approach is gradually bringing AI closer to autonomous cyberdefense systems.
Reduce response time to security breaches
One of the main challenges in cybersecurity is the speed of response. It can sometimes take several days from the time a vulnerability is identified through its analysis, the validation of the patch, and its deployment. This delay leaves attackers with a significant window of opportunity to exploit the vulnerability.
Daybreak aims specifically to reduce this time to just a few minutes for certain types of vulnerabilities. Thanks to its automated analysis capabilities, the AI can quickly scan through large volumes of code, identify known vulnerability patterns, and immediately suggest potential fixes.
This approach could have a major impact in DevSecOps environments, where teams are already seeking to integrate security directly into software development cycles. AI thus becomes an operational accelerator capable of providing continuous support to developers and cybersecurity teams.
The Rise of Agent-Based AI in Cybersecurity
Daybreak is a prime example of the emergence of agent-based AI in cybersecurity. Unlike traditional generative models, which are limited to text generation, agent-based systems are capable of executing complex sequences of actions in a semi-autonomous manner.
In the case of Daybreak, this means that the AI can:
- analyze a software environment,
- identify vulnerabilities,
- generate patches,
- verify certain results,
- and propose implementation steps.
This approach is fundamentally transforming the way cybersecurity tools operate. AI no longer merely alerts humans; it is directly involved in the operational execution of certain technical tasks.
This development is part of a broader trend observed across the technology industry, as AI models are gradually evolving into systems capable of taking action rather than simply responding.
A response to the surge in attacks and data volume
Cybersecurity teams today are facing a massive increase in attack surfaces and the volume of data to be analyzed. According to Cybersecurity Ventures, the cost of cybercrime could exceed $10.5 trillion annually by 20272.
In this context, automation has become almost indispensable. Human analysts can no longer monitor complex cloud infrastructures, thousands of applications, and a constant stream of security events on their own. AI thus emerges as a way to enhance detection and response capabilities without proportionally expanding teams.
OpenAI appears to be positioning itself in a rapidly expanding strategic market: that of AI-enhanced cybersecurity platforms.
A strategic battle between OpenAI, Anthropic, Google, and Microsoft
The launch of Daybreak is part of a broader race in the field of AI cybersecurity. Major tech companies are investing heavily in tools capable of automating threat detection and securing infrastructure.
Microsoft is already developing Security Copilot, Google is enhancing its Gemini tools for cloud security, and Anthropic is also working on systems specialized in cyber defense analysis. This competition demonstrates that cybersecurity is becoming one of the primary areas of application for agent-based AI.
What sets Daybreak apart is its operational focus. OpenAI is not merely seeking to produce analyses or recommendations, but to create a system capable of responding quickly in real-world environments to accelerate remediation processes.
AI capable of correcting… but also potentially exploiting
The emergence of systems like Daybreak also highlights a significant paradox in the application of artificial intelligence to cybersecurity. The very capabilities that enable AI to detect and fix vulnerabilities can also be used to exploit them.
An agent capable of analyzing code, identifying vulnerabilities, and interacting with systems could theoretically be misused for malicious purposes. This duality explains why AI labs are investing so heavily in security, alignment, and technical safeguards.
Recent discussions about AI systems capable of exploiting vulnerabilities or creating autonomous sub-agents show that the line between cyber defense and offensive cybersecurity is becoming increasingly blurred as the capabilities of these models advance.
The Limitations and Risks of Automated Cybersecurity
Despite its promises, Daybreak does not eliminate the need for human oversight. Automated systems can produce false positives, generate inappropriate fixes, or misinterpret certain complex configurations.
In critical infrastructure, an improperly applied automatic fix can cause:
- service interruptions,
- software incompatibilities,
- or additional vulnerabilities.
AI therefore remains an advanced support tool rather than a complete replacement for cybersecurity experts. Human analysts continue to play a central role in:
- the approval of decisions,
- strategic analysis,
- the management of complex incidents,
- and overall oversight of the systems.
Toward Infrastructure Protected by AI Agents
With Daybreak, OpenAI demonstrates that the future of cybersecurity may increasingly rely on AI agents capable of intervening in real time within digital infrastructures. This trend goes hand in hand with the rise of cloud environments, distributed architectures, and increasingly complex software systems.
The key issue in the coming years will likely not be whether AI will play a role in cybersecurity, but rather how far its autonomy can be expanded without compromising human control. Daybreak thus marks a new milestone in the transformation of cyber defense, where AI agents are gradually becoming technical operators capable of directly interacting with systems.
How does Daybreak work?
Daybreak is built on an agentic AI architecture specialized in offensive and defensive cybersecurity. Developed by OpenAI, the system combines advanced language models with automated analysis mechanisms capable of inspecting code, detecting vulnerabilities and proposing fixes in real time. Unlike traditional cybersecurity tools, which are often limited to flagging anomalies or generating alerts, Daybreak acts as an operational agent capable of carrying out multiple analysis and remediation steps semi-autonomously.
The system works as an intelligent layer of oversight and intervention on top of digital infrastructure. The AI can analyze code repositories, cloud environments, system configurations or activity logs to identify suspicious behavior or known vulnerabilities. Once vulnerabilities are detected, the model can generate remediation recommendations, propose patches and assist cybersecurity teams with remediation operations. This approach combines natural language processing, behavioral analysis, workflow automation and multi-step reasoning.
- Automated vulnerability detection: analysis of risky code and configurations
- Fix generation: proposed patches and remediation recommendations
- Behavioral analysis: identification of abnormal activity in systems
- DevSecOps integration: security built directly into development cycles
- Continuous monitoring: real-time monitoring of infrastructure and applications
- Conversational interaction: driving cyber analyses in natural language
- Workflow automation: execution of multi-step security action chains
- Autonomous analysis of systems and digital environments
- Understanding of relationships between software components
- Suggested actions tailored to the detected context
- Human validation of critical fixes
- Full traceability of actions performed by the AI
- Separation of test and production environments
- Ability to undo certain automated operations
- Analysis of GitHub repositories
- Connection to cloud infrastructure
- Use of SIEM logs
- Integration with DevOps and DevSecOps environments
- Connection to monitoring platforms
- Unified view of connected security systems
- Risk of false positives on certain complex vulnerabilities
- Potentially unsuitable fixes without human validation
- Difficulty analyzing highly customized environments
- Dependence on the quality of available data and logs
- High computational cost for continuous monitoring
- Risk of automated capabilities being repurposed for offensive use
- Need for human oversight of critical systems
Learn more
The emergence of systems capable of automatically identifying and fixing vulnerabilities highlights the growing integration of artificial intelligence into advanced cybersecurity strategies. On a related topic, check out our article “AI Systems Capable of Self-Replication: A New Challenge for Cybersecurity”, which analyzes the new risks associated with the autonomy of intelligent systems and the related control challenges.
References
1. IBM. (2025). Cost of a Data Breach Report.
https://www.ibm.com
2. Cybersecurity Ventures. (2025). Cybercrime Damage Costs Report.
https://cybersecurityventures.com